Architecting Dual-Mode Hybrid TLS 1.3 for ISO 8583 Payment Switches

- Lattice-based TLS handshakes push ClientHello and Certificate payloads beyond the 1,500-byte TCP MTU limit, triggering packet fragmentation.
- TCP fragmentation causes retransmissions and latency spikes that breach internal sub-10ms processing SLAs and cause switch timeout cascades.
- Dual-mode ingestion architecture utilizes persistent TCP connection pooling with 0-RTT session resumption to eliminate per-transaction handshake overhead.
- RFC 8879 certificate compression (zstd/brotli) compresses post-quantum certificate chains to keep payloads safely under MTU boundaries.
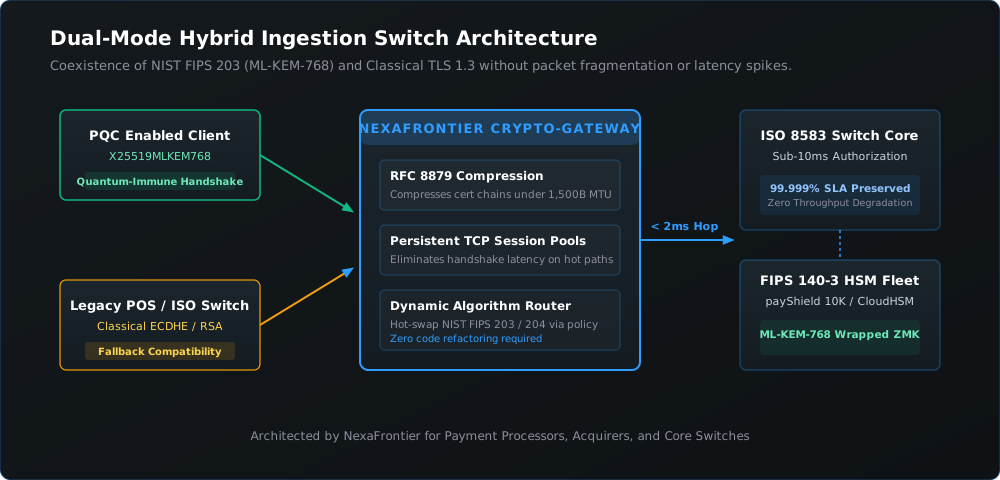
Running hybrid TLS 1.3 on an ISO 8583 switch is a packet-budget exercise before it is a cryptography exercise. A hybrid X25519MLKEM768 ClientHello typically exceeds the 1,500-byte Ethernet MTU, so the design goal is to keep post-quantum material out of the hot path through RFC 8879 certificate compression, persistent connection pooling, and dual-mode edge proxies rather than to tune OpenSSL and hope.
The Latency Budget and the 1,500-Byte Wall
Core authorizers operate under scheme-enforced end-to-end timeouts, commonly quoted around 2,000ms, with individual internal switch hops constrained to sub-10ms. That budget assumes small messages and predictable network behavior. A standard Ethernet MTU is 1,500 bytes, leaving roughly 1,460 bytes of usable TCP payload after IP and TCP headers. Anything above that fragments across multiple packets and invites retransmissions and window stalls, so the protocol overhead of the handshake competes directly with the latency budget.
Worked Example: What Fits in One Segment
The hybrid key share alone is the problem. Multipliers are given against a stated baseline.
| Handshake element | Size | Baseline note |
|---|---|---|
| Classical X25519 key share | 32 bytes | Baseline |
| ML-KEM-768 encapsulation key share | 1,184 bytes | 37x a 32-byte X25519 share |
| Hybrid X25519MLKEM768 key share | 1,216 bytes | 38x a 32-byte X25519 share |
| Typical ClientHello after suites and extensions | roughly 1,600 to 1,900 bytes | Exceeds the roughly 1,460-byte usable payload |
| Certificate chain (uncompressed, post-quantum) | Several kilobytes | Multiple segments |
An ML-KEM-768 encapsulation key is 1,184 bytes - 37x a 32-byte X25519 share - and the combined hybrid share is 1,216 bytes, or 38x the classical share. Added to the record header, handshake header, random, session ID, cipher-suite list, and extension block, a full hybrid ClientHello lands above the 1,460-byte usable payload and fragments. Under peak volumes, retransmission-driven stalls of 10 to 15ms per handshake cascade into timeout penalties and scheme SLA exposure.
Handshake Cost Versus Steady-State Cost
The critical distinction is between the one-time handshake and per-transaction steady state. Hybrid key exchange inflates the handshake, not the record payload; once a pooled tunnel is established, ISO 8583 messages travel inside symmetric AES-GCM records whose size is essentially unchanged. That is why pooling is the highest-leverage control: it amortizes an expensive handshake across thousands of transactions.
| Phase | Classical | Hybrid X25519MLKEM768 | Mitigation |
|---|---|---|---|
| New handshake | Fits one segment | Spans multiple segments | Pool and resume connections |
| Certificate flight | Moderate | Several kilobytes | RFC 8879 zstd compression |
| Steady-state record | AES-GCM | AES-GCM, unchanged | None required |
RFC 8879 Certificate Compression with zstd
Certificate payloads dominate the later flight, and they are compressible. RFC 8879 defines TLS certificate compression; using zstd, with brotli as an alternative, typically reduces post-quantum certificate chains by roughly 40% to 55%. That keeps the server flight inside fewer segments and removes much of the retransmission risk introduced by larger keys. Compression applies to the certificate message specifically, so it does not perturb the key share; the two controls are complementary.
Worked Example: Amortizing One Handshake
If a pooled connection carries N transactions, the per-transaction handshake cost is the handshake cost divided by N. A hybrid handshake that spans three segments instead of one adds a fixed cost, but pooling across a production burst turns that fixed cost into a rounding error. The table makes the trade explicit.
| Handshakes per 10,000 transactions | Relative handshake overhead |
|---|---|
| 10,000 (one per transaction) | Baseline, highest |
| 100 (pooled 100x) | About 1% of baseline |
| 10 (pooled 1,000x) | About 0.1% of baseline |
Detecting Fragmentation in the Field
Fragmentation is visible before latency degrades if you watch the right counters. Track TCP retransmission rate, segments per handshake, and the distribution of handshake completion time rather than only the average. A rising retransmit rate on handshake flights, with steady application traffic, is the earliest signal that post-quantum material has pushed a frame past the MTU. Correlating that with the internal hop latency histogram localizes the problem to a specific route or terminator.
Three Architectural Levers
- Persistent connection pooling with session resumption. Maintain pre-negotiated hybrid TLS 1.3 tunnels and use 0-RTT resumption where it is compliant with PCI SSC session and replay rules. The cheapest handshake is the one you never perform per transaction.
- RFC 8879 compression. Compress certificate chains with zstd so the negotiation fits within the MTU envelope.
- Dual-mode edge proxies. Terminate quantum-safe hybrid TLS at dedicated Envoy or NGINX edge proxies and route bare ISO 8583 messages over isolated internal links, so the switch core is untouched by handshake size.
A Reference Migration Plan
- Baseline current handshake sizes and hop latencies on representative links.
- Enable certificate compression and confirm the reduction is within the expected range.
- Introduce connection pooling so handshakes are amortized rather than per transaction.
- Enable hybrid negotiation on a limited route and measure fragmentation and retransmits.
- Expand to all routes once latency stays inside the sub-10ms internal budget.
- Re-run the packet estimator after any MTU or certificate-chain change.
Measure Before You Cut Over
Do not estimate fragmentation from theory. Model handshake expansion and the latency penalty against the 1,500-byte MTU with a purpose-built estimator, then confirm with a synthetic load harness at production concurrency before enabling hybrid negotiation in a live window.
Failure Modes to Avoid
- Enabling hybrid negotiation globally without checking MTU handling end to end.
- Forcing a full handshake per transaction instead of pooling connections.
- Leaving certificate chains uncompressed on latency-sensitive routes.
- Removing classical fallback before upstream partners support ML-KEM.
Key Takeaways
- A hybrid X25519MLKEM768 share is 1,216 bytes - 38x a 32-byte X25519 share - and pushes ClientHello past the 1,500-byte MTU.
- RFC 8879 compression with zstd typically cuts certificate chains by 40% to 55%.
- Connection pooling plus 0-RTT removes most handshake exposure; dual-mode edge proxies protect the switch core.
- Benchmark against the MTU before cutover, not after a timeout cascade.
Frequently Asked Questions
Larger post-quantum public keys and signatures exceed standard MTU boundaries, triggering multi-packet fragmentation and multi-millisecond handshake delays that cause sub-100ms ISO 8583 authorizers to breach SLAs.
By enabling RFC 8879 certificate compression (zstd/brotli), maintaining pre-negotiated persistent connection pools, and deploying dual-mode edge crypto-proxies.
It is the standardized hybrid key exchange combining fast classical ECDH with NIST FIPS 203 ML-KEM, ensuring continuous compliance and quantum resistance.
Subscribe for Technical Briefings & PQC Advisories
Stay ahead of NIST FIPS standardizations, PCI DSS v4.0+ mandates, and quantum vulnerability disclosures.
Connect With Our Cryptographic Engineering Team
Discuss PQC migration strategies, HSM key lifecycle hierarchies, or schedule a fixed-scope Cryptographic Discovery Audit for your enterprise payment pipeline.

