Migrating Payment Hardware Security Modules (HSMs) to NIST FIPS 203 ML-KEM

- NIST FIPS 203 ML-KEM-768 keys (1,184-byte public key) represent a 4x–37x payload expansion over classical ECC/RSA keys in physical HSM secure storage.
- Legacy HSM units face Non-Volatile Memory (NVM) buffer exhaustion and host command overflow across PKCS#11 and proprietary TCP interfaces.
- Zone Master Key (ZMK) hierarchies must be re-architected with hybrid key encapsulation to prevent PIN translation compromises.
- Modernization requires FIPS 140-3 firmware verification and synthetic load testing to safeguard sub-10ms peak authorization throughput.
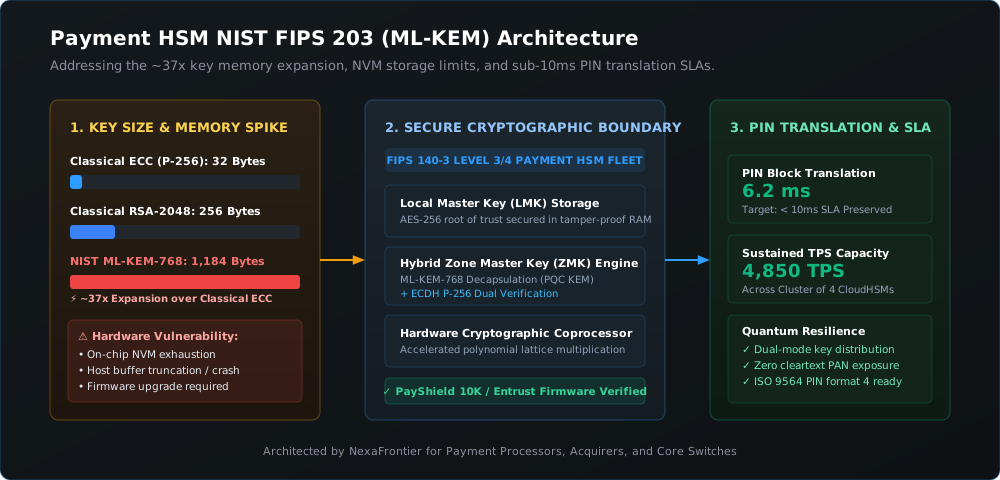
Migrating payment HSMs to FIPS 203 ML-KEM is less a mathematics problem than a memory-and-buffer problem. The ML-KEM-768 key material is fixed by the standard - a 1,184-byte public key and a 1,088-byte ciphertext - but the HSM host interfaces, non-volatile memory budgets, and TR-31 key-block columns that must carry it were sized for classical keys one to two orders of magnitude smaller. The migration succeeds when you change where keys live, not just which algorithm generates them.
Why HSM Migration Differs From Software PQC
In software, larger keys cost bandwidth and a little CPU. Inside a Thales payShield 10K, an Utimaco Atalla AT1000, or an AWS CloudHSM cluster, they cost non-volatile memory capacity, fixed-size command buffers, and per-operation overhead that shows up directly in authorization latency. HSM firmware is validated and, in payment environments, certified; you cannot simply patch a buffer size in production. Every change follows a vendor release train and a certification cycle, which is why HSM migration is scheduled in quarters, not sprints.
The Arithmetic of Lattice Key Bloat
Multipliers below are stated against an explicit baseline so they can be audited against vendor data sheets.
| Material | Size | Comparison |
|---|---|---|
| Ed25519 key (baseline) | 32 bytes | 1x |
| RSA-2048 public key | 256 bytes | 8x a 32-byte Ed25519 key |
| ML-KEM-768 public key | 1,184 bytes | 37x a 32-byte Ed25519 key; 4.6x an RSA-2048 key |
| Classical TR-31 key block | roughly 160 bytes | Baseline for the 7.4x figure |
| ML-KEM-768 public key vs TR-31 block | 1,184 vs roughly 160 bytes | 7.4x expansion |
| ML-KEM-768 ciphertext | 1,088 bytes | 4.25x a 256-byte RSA-2048 ciphertext |
The headline number is 7.4x: an ML-KEM-768 public key is 1,184 bytes, a 7.4x expansion over a classical TR-31 key block of roughly 160 bytes, and 37x a 32-byte Ed25519 key. Neither figure is a rounding curiosity; both translate directly into capacity and column-width decisions.
Where HSM Memory and Buffers Break
The failure modes are predictable and worth naming before they appear in a peak window.
- Non-volatile memory exhaustion. Legacy units hold a finite number of keys; storing post-quantum material inline consumes the budget several times faster than the classical equivalent.
- Command buffer overflow. PKCS#11 and proprietary TCP host commands use fixed request sizes; an oversized key block can exceed them and return hard errors rather than graceful degradation.
- Throughput degradation. Larger payloads increase serialization time per operation, which compounds under Black Friday-scale concurrency.
- Database truncation. TR-31 key blocks written to fixed 256-byte or 512-byte columns overflow when the material grows, which can fault a switch rather than merely log an error.
Worked Example: A Single ZMK Rotation
Consider rotating a Zone Master Key across an HSM fleet. With classical TR-31 blocks the payload fits comfortably in existing host command frames. Substituting an inline ML-KEM-768 public key changes every step of the operation.
| Step | Classical | Post-quantum inline | Post-quantum pointer |
|---|---|---|---|
| Key material on the wire | Roughly 160-byte TR-31 block | 1,184-byte ML-KEM-768 key | 32-byte pointer plus vault fetch |
| Database column fit | Fits a 256-byte column | Overflows narrow columns | Fits a 256-byte column |
| Host command frame | Within fixed buffer | Risk of buffer overflow | Within fixed buffer |
| Operational key use | AES or TDES | AES for PIN translation | AES for PIN translation |
The pointer column is the point: a 32-byte identifier resolves through a microsecond-latency in-memory cache to the full 1,184-byte envelope held in an external vault, so neither the database nor the host command path ever carries the expanded key.
The Pointer Architecture for ZMK Hierarchies
The clean solution is to stop storing full key blocks inline. Replace them with a compact 32-byte key pointer that resolves, through a microsecond-latency in-memory cache, to the full ML-KEM-768 envelope held in an external, HSM-governed cryptographic vault. The switch database keeps its narrow columns; the vault absorbs the growth; the host command path stays small. Zone Master Key distribution then wraps the exchange with a hybrid KEM envelope (ML-KEM-768 plus AES-256 key wrap) while retaining AES for sub-millisecond operational PIN translation, where symmetric performance remains the right tool.
The Certification Clock
Two dates drive the schedule. PCI SSC published PCI PTS HSM v5.0 on May 18, 2026, adding post-quantum considerations and updated cryptographic requirements for payment hardware. Separately, NIST moves the remaining FIPS 140-2 module validations to Historical on September 21, 2026, after which new modules must be FIPS 140-3 validated. Firmware roadmaps that ignore either date will create procurement gaps, because a certified module is a prerequisite for the audits that follow.
A Phased Modernization Roadmap
- Firmware matrix. Map every HSM model and firmware level against FIPS 140-3 and PCI PTS HSM v5.0 support, and flag units with no PQC upgrade path.
- Vault and pointer design. Stand up the external cryptographic vault and the 32-byte pointer scheme before generating any ML-KEM key material.
- Hybrid wrapping. Move ZMK distribution to hybrid envelopes while leaving AES in place for operational symmetric work.
- Load harness. Benchmark full post-quantum negotiation under synthetic load before production cutover, not after.
- Re-inventory. Feed the new key locations into the cryptographic inventory so PCI DSS evidence stays current.
What to Benchmark Before Cutover
A synthetic harness should measure four things, because each maps to a different operational risk.
- Handshake latency with and without hybrid groups enabled.
- Key-generation and key-import time for ML-KEM-768 material on each HSM model.
- Peak throughput in operations per second at production concurrency.
- Error rates and timeout counts as buffers approach their limits.
Key Takeaways
- ML-KEM-768 fixes a 1,184-byte public key and a 1,088-byte ciphertext; the engineering problem is where those bytes live.
- 1,184 bytes is 37x a 32-byte Ed25519 key and 7.4x a roughly 160-byte classical TR-31 key block.
- 32-byte pointers to an external HSM-governed vault prevent non-volatile memory exhaustion and column truncation.
- PCI PTS HSM v5.0 (May 18, 2026) and the FIPS 140-2 sunset (September 21, 2026) bound the timeline.
Frequently Asked Questions
Lattice-based public keys (1,184 bytes for ML-KEM-768) are up to 37 times larger than 32-byte ECC keys. This expansion strains internal HSM memory, increases command serialization times, and requires re-architected host connection pooling.
Leading payment HSM providers including Thales (payShield 10K), Entrust (nShield), and AWS CloudHSM have published post-quantum roadmaps supporting NIST FIPS 203/204 algorithms under FIPS 140-3 certification tracks.
By wrapping ZMK distribution payloads with hybrid key encapsulation (ML-KEM-768 + AES-256 Key Wrap) while maintaining high-speed symmetric AES for operational PIN blocks.
Subscribe for Technical Briefings & PQC Advisories
Stay ahead of NIST FIPS standardizations, PCI DSS v4.0+ mandates, and quantum vulnerability disclosures.
Connect With Our Cryptographic Engineering Team
Discuss PQC migration strategies, HSM key lifecycle hierarchies, or schedule a fixed-scope Cryptographic Discovery Audit for your enterprise payment pipeline.

