PCI DSS v4.0+ Cryptographic Bill of Materials (CBOM): Implementation Guide

- PCI DSS Requirement 4.2.1.1 and 12.3.3 strictly enforce documented cryptographic inventories across the entire Cardholder Data Environment (CDE).
- A production-grade CBOM maps Asset Location, Cipher Suite Primitives, Key Lifecycles, and Quantum Vulnerability Scores.
- Automating CBOM generation via passive network inspection and TLS endpoint scanning produces compliant OWASP CycloneDX 1.6 artifacts.
- A 14-day CBOM Discovery Audit gives CISOs and QSA auditors an auditable blueprint to pass compliance reviews with zero business disruption.
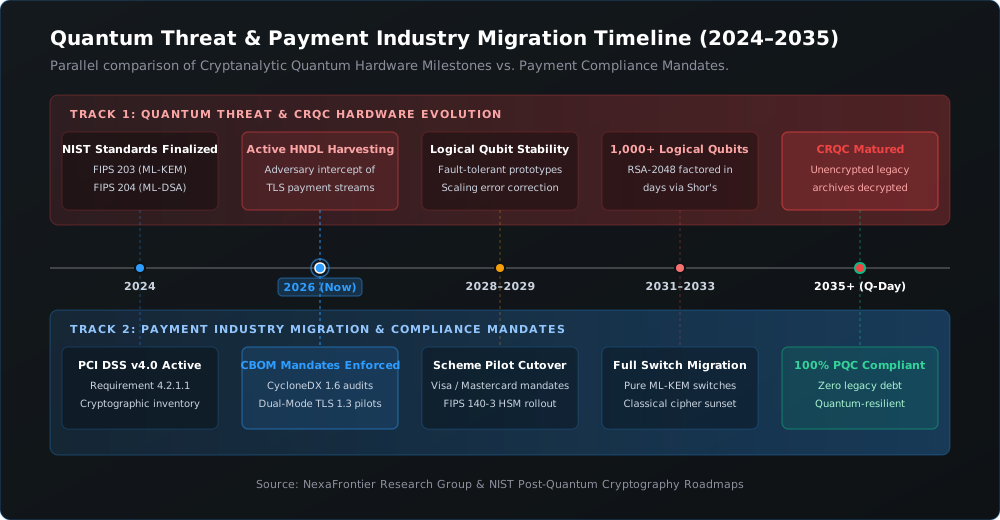
PCI DSS v4.0.1 does not require a Cryptographic Bill of Materials by name, but it does require the two things a CBOM operationalizes: an inventory of the keys and certificates protecting cardholder data (Requirement 4.2.1.1) and a documented inventory of cipher suites and protocols reviewed at least annually (Requirement 12.3.3). Both became mandatory on March 31, 2025. A machine-readable CycloneDX 1.6 CBOM is the practical way to produce that evidence continuously rather than rebuilding a spreadsheet each audit cycle.
What the Requirements Actually Say
Requirement 4.2.1.1 asks for an up-to-date inventory of trusted keys and certificates used to protect PAN. Requirement 12.3.3 asks for a documented inventory of cryptographic cipher suites and protocols in use, with an annual review and a deprecation path. The standard does not prescribe a format. That is the opening: a static spreadsheet is technically permitted and practically fragile, because it drifts the moment a certificate renews or a dependency updates. A machine-readable inventory can be regenerated and diffed, which turns the annual review into a comparison rather than a discovery project.
What Belongs in a Production CBOM
A useful CBOM documents four dimensions for every service, database, and network link in the Cardholder Data Environment.
| Dimension | Example values |
|---|---|
| Asset location and owner | Service, container, ingress controller, or HSM partition |
| Primitive and parameters | KEM (RSA, ECDH, ML-KEM-768), signature (ECDSA, ML-DSA-65), symmetric (AES-256-GCM), hash (SHA-256, SHA-3) |
| Key lifecycle | Key length, rotation cadence, generation origin, certificate validity |
| Quantum vulnerability class | Classical, Hybrid, or Pure PQC (FIPS 203/204) |
The size facts that make this matter are worth stating with their baselines: an ML-KEM-768 public key is 1,184 bytes, which is 37x a 32-byte Ed25519 key. That ratio is exactly the kind of entry a CBOM must capture so that downstream network and database teams can plan for MTU and column-width effects before a post-quantum cutover.
Worked Example: One CBOM Entry
A single entry for an authorization service might resolve as follows. Every field is machine-readable, so a diff between two builds can flag change without human inspection.
| Field | Value |
|---|---|
| Asset | auth-gateway-01 ingress TLS terminator |
| Key encapsulation | X25519MLKEM768 |
| Signature | ECDSA P-256 (post-quantum migration pending) |
| Symmetric | AES-256-GCM |
| Key length note | 1,184-byte ML-KEM-768 encapsulation key |
| Quantum class | Hybrid |
Choosing CycloneDX 1.6
OWASP CycloneDX 1.6 is a machine-readable JSON or XML schema that represents cryptographic assets as components, including algorithm identifiers, key length, certificate expiry, cipher mode, and a quantum vulnerability indicator. Because it belongs to the same format family used for SBOMs, it plugs into existing CI/CD tooling and can be diffed between builds. That reuse matters: teams already generating an SBOM for dependency management can extend the same pipeline rather than standing up a separate cryptographic inventory system.
A Repeatable Discovery Workflow
- Passive inspection. Use out-of-band SPAN or TAP capture with tshark filters that extract TLS handshake records and drop application payload, so no PAN data is inspected.
- Endpoint probing. Probe internal and external TLS terminators with OpenSSL 3.5+ to enumerate supported groups (including X25519MLKEM768), cipher suites, and certificate chains.
- Sanitized configuration ingestion. Pull cryptographic settings from NGINX, Envoy, HAProxy, and API gateways through local scripts that strip private keys, credentials, and addresses before transmission.
- Dependency parsing. Ingest SBOMs and lockfiles to find libraries pinned to cryptographic providers that lack FIPS 203 and 204 support.
- CI/CD hooks. Wire GitHub Actions or GitLab CI to regenerate the CBOM on every merge so drift is detected at build time.
Evidence, Not Artifacts
The value of a CBOM is in its freshness. A one-time export satisfies a checkbox until the next certificate rotation. A continuously regenerated CBOM, with diffs that show when a classical-only cipher reappears, gives a Qualified Security Assessor evidence of ongoing control rather than a snapshot of intent. That is also the natural bridge to post-quantum planning: the same inventory that satisfies 4.2.1.1 and 12.3.3 identifies which entries are quantum-vulnerable and in what order to migrate them.
Running the Annual Review
Requirement 12.3.3 is a review obligation, not merely a data obligation. A defensible review names an owner, compares the current inventory against the previous one, records every newly introduced algorithm, and documents a removal date for each deprecated entry. Automating the inventory reduces the review to a diff and a decision log, which is far easier to evidence than a manual reconciliation.
From Inventory to Deprecation Roadmap
An inventory that lists algorithms without a removal plan does not satisfy the spirit of Requirement 12.3.3. Each deprecated primitive should carry a target date and an owner, and the CBOM should be the authoritative source for that plan. A practical pattern is to tag each entry with a lifecycle state - active, migrate, or deprecated - and to fail a build when a deprecated primitive appears in a newly introduced component. That converts the inventory from a report into a control.
Scope Boundaries
Two scope decisions determine whether the CBOM is defensible. First, the boundary of the Cardholder Data Environment must be explicit, because keys and certificates outside it are not in scope for 4.2.1.1. Second, internal service-to-service TLS must be included even when it does not cross the perimeter, because those links often protect PAN in motion. Documenting those boundaries up front prevents the most common assessor finding: a comprehensive-looking inventory that quietly omits half the environment.
Common Findings to Pre-empt
- Inventory covers the perimeter but omits internal service-to-service TLS.
- Certificate expiry is tracked but key length and algorithm are not.
- No named owner for review, so the annual requirement lapses.
- Deprecated ciphers are listed but have no removal date.
Key Takeaways
- Requirements 4.2.1.1 and 12.3.3 have been mandatory since March 31, 2025; no format is mandated.
- CycloneDX 1.6 makes the required inventories machine-readable and diffable.
- Discovery combines passive capture, endpoint probing, sanitized config ingestion, and dependency parsing.
- Continuously regenerated evidence beats a static spreadsheet every audit cycle.
Frequently Asked Questions
A CBOM is a structured, machine-readable inventory (such as OWASP CycloneDX 1.6) cataloging every algorithm, key length, certificate, protocol, and cipher suite active across an organization's systems.
Requirement 4.2.1.1 mandates that entities maintain an up-to-date inventory of all cryptographic suites used to protect cardholder data. A CBOM directly fulfills this audit artifact requirement.
With automated passive network inspection and endpoint scanning, NexaFrontier produces a comprehensive CBOM in a fixed 14-day discovery sprint.
Subscribe for Technical Briefings & PQC Advisories
Stay ahead of NIST FIPS standardizations, PCI DSS v4.0+ mandates, and quantum vulnerability disclosures.
Connect With Our Cryptographic Engineering Team
Discuss PQC migration strategies, HSM key lifecycle hierarchies, or schedule a fixed-scope Cryptographic Discovery Audit for your enterprise payment pipeline.

